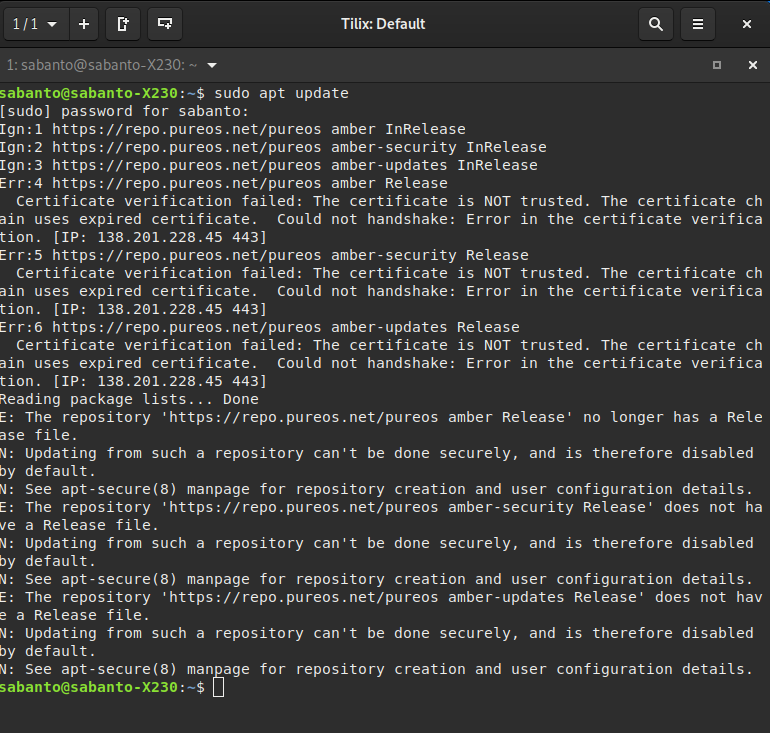
I am sure its easy but i do not know how to fix this issue.
Help will be appreciated
Ign:1 https://repo.pureos.net/pureos amber InRelease
Ign:2 https://repo.pureos.net/pureos amber-security InRelease
Ign:3 https://repo.pureos.net/pureos amber-updates InRelease
Err:4 https://repo.pureos.net/pureos amber Release
  Certificate verification failed: The certificate is NOT trusted. The certificate chain uses expired certificate.  Could not handshake: Error in the certificate verification. [IP: 138.201.228.45 443]
Err:5 https://repo.pureos.net/pureos amber-security Release
  Certificate verification failed: The certificate is NOT trusted. The certificate chain uses expired certificate.  Could not handshake: Error in the certificate verification. [IP: 138.201.228.45 443]
Err:6 https://repo.pureos.net/pureos amber-updates Release
  Certificate verification failed: The certificate is NOT trusted. The certificate chain uses expired certificate.  Could not handshake: Error in the certificate verification. [IP: 138.201.228.45 443]
Reading package lists... Done
E: The repository 'https://repo.pureos.net/pureos amber Release' no longer has a Release file.
N: Updating from such a repository can't be done securely, and is therefore disabled by default.
N: See apt-secure(8) manpage for repository creation and user configuration details.
E: The repository 'https://repo.pureos.net/pureos amber-security Release' no longer has a Release file.
N: Updating from such a repository can't be done securely, and is therefore disabled by default.
N: See apt-secure(8) manpage for repository creation and user configuration details.
E: The repository 'https://repo.pureos.net/pureos amber-updates Release' no longer has a Release file.
N: Updating from such a repository can't be done securely, and is therefore disabled by default.
N: See apt-secure(8) manpage for repository creation and user configuration details.
Thank you
It is a curious thing - after all this is the repositories for PureOS software.
So all the people who are using PureOS cannot update and upgrade their PureOS??
Thanks for pointing this out. I’ll take another look at our certificates which do expire from time to time. But the redirect is on purpose. Also, in general, it is a good idea to run apt update after a new installation of PureOS (or any Debian based distro.)
It’s worth mentioning that using the http repos does not reduce your security though it may reduce your confidentiality until you install apt-transport-https.
Ok thanks for both replies @jeremiah
I simply installed PureOS 9 and immediately update and just got the error message from the system. It all took place today morning time in the UK
Is the clock of your system set correctly?
It might happen you get issues with establishing TLS connections when the time is off, then I expect you would see TLS error messages wile browsing other sites too.
Yes, that’s fine. My point, perhaps not well made, was that I wouldn’t get a redirect at all if the certificate is no good! The client would not be able to complete the SSL handshake at all, and hence I would not be able to issue the HTTP GET command, much less receive any response.
The certificate date looks fine (basically the September/October/November certificate) - so unlikely to have expired in the last day or so, or to have been updated in the last day or so.
So I am still left wondering whether there was a glitch on the client side or someone was temporarily messing with the repo on the server side or, dare I say it, someone was attempting to MITM the OP.
Adding: PS source.puri.smis producing a complaint about an expired certificate.
I have had the same issue on my laptop for the last 3 days. I can’t install software from the pure OS software center, I can’t update my system either. I was able enable flatpaks, which is the only way to install something on my system. All terminal commands to update and install are failed due to “certificate NOT trusted” errors.
Yes my clock is set correctly, I have rebooted several times, tried different ethernet connections & even usb tethering from my phone. I have tried all the terminal commands to update & upgrade. All terminal commands fail to the same certificate NOT trusted error. I was just about to re-install my OS from scratch but decided to check the forum before I did.
I am willing and able to install the beta version of Pure OS if it will correct the issue. What can I do to correct this error?
You don’t need to do anything, nor can you realistically.
You wait until the server end resolves the issue. You can see from the above posts that this issue has “director level” attention!
However it may now already be fixed because I see “Validity Not Before Wed, 06 Oct 2021 05:35:40 GMT” for Purism’s repo certificate i.e. freshly baked.
Can you use the command line? If so, you can try to run sudo apt update (it’ll ask you for your password which you can safely give.) I just did this on a local Amber (PureOS 9) system and I was able to update successfully.
Hi Jeremiah, Thank you for your response. I did try the sudo apt update command. It still does not work for me. Here is a screen shot of my tilix session trying the command & the results.
One option might be to use the http: repo for the first apt-get update and then switch back to the https: repos. While you lose a little confidentiality, you won’t lose any security because the packages themselves are signed with PureOS’ key.
Thank you again, I tried those terminal commands and it did not fix the certificate issue. However I just did a fresh install of Byzantium and everything is working fine. My certificate errors were on amber. Thanks for all the help.